Firewall Vulnerability: 4 Critical Flaws to Patch Now
Firewall Vulnerability: 4 Critical Flaws to Patch Now
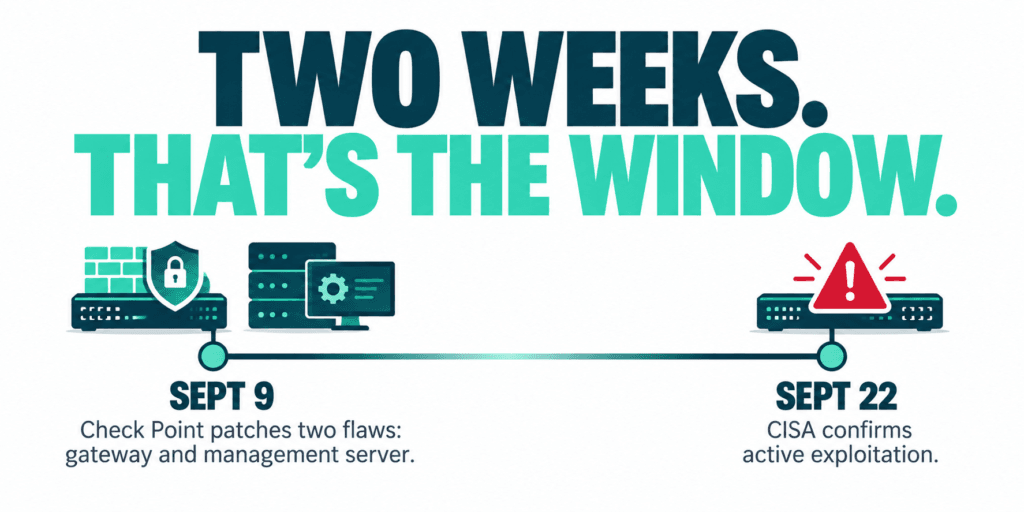
A firewall vulnerability rated 9.8 out of 10 was patched by Check Point on September 9. There was no confirmed attack at the time, just a warning from the Dutch government’s cyber security centre that exploitation looked imminent. On September 22, CISA confirmed it, and added a second Check Point flaw alongside it. That two week gap between disclosure and confirmed exploitation is the whole story here, and it says more about patch timing than about any one vendor.
What This Firewall Vulnerability Actually Does
Check Point actually shipped two separate patches on September 9, for two different vulnerabilities on two different parts of its product line.Check Point actually shipped two separate patches on September 9, for two different vulnerabilities on two different parts of its product line.
CVE-2026-85102 is the flaw in the Security Gateway itself, the device handling live VPN traffic. It’s a flaw in how the gateway validates certificates during VPN negotiation. Get past that check and an unauthenticated attacker can run code directly on the gateway, no login required.
CVE-2026-93616 sits somewhere different: the Security Management Server, the console that controls policy, logs, and configuration across a Check Point deployment (also affects Multi-Domain Security Management Server, Log Server, Multi-Domain Log Server, and SmartEvent). It’s a path traversal flaw that lets an unauthenticated attacker upload and execute arbitrary scripts on the management server, fixed separately through Check Point’s R82.20 Security Hotfix, not the same patch that covers the gateway flaw.
That distinction matters operationally. Patching the gateway doesn’t patch the management server, and vice versa. A business running Check Point needs to confirm both planes are current, not just one.
Check Point found and disclosed both issues itself, and shipped fixes the same day. No evidence of active exploitation at the time of disclosure. By September 12, Check Point had started observing exploitation attempts against Spark firewall customers using anonymizing infrastructure. By September 22, CISA had confirmed active exploitation of both and added them to its Known Exploited Vulnerabilities catalog with a federal remediation deadline of September 25, as SecurityAffairs reported.
The same week, CISA added two more network edge products to its confirmed exploited list: a flaw in Arista’s VeloCloud Orchestrator, and one in F5’s BIG-IP APM. Four vulnerabilities, three vendors, one week, the same lesson each time. Attackers probe internet facing network gear first, because it’s the thing standing between them and everything behind it.
Why This Matters for a Small or Midsize Business?
These aren’t obscure enterprise products. Firewalls, VPN gateways, and the management consoles that control them are exactly what a small business relies on to guard its perimeter, often without a dedicated security team watching vendor bulletins day to day. A firewall vulnerability like this doesn’t need an employee to click a link or fall for a phishing email. It just needs the device to be reachable and unpatched.
The Real Gap Isn’t the Vendor, It’s the Patch Window
Check Point did everything right here. Found both issues itself, disclosed them, shipped fixes the same day, no delay. The businesses at risk right now aren’t the ones using Check Point. They’re the ones still running the unpatched build two weeks later, whether or not anyone on staff knew a patch existed, or knew there were two patches to apply instead of one.
That’s true of any vendor, not just this one. A 9.8 severity rating is urgent the day it’s published, not the day it shows up on a government watchlist.
What to Check This Week?
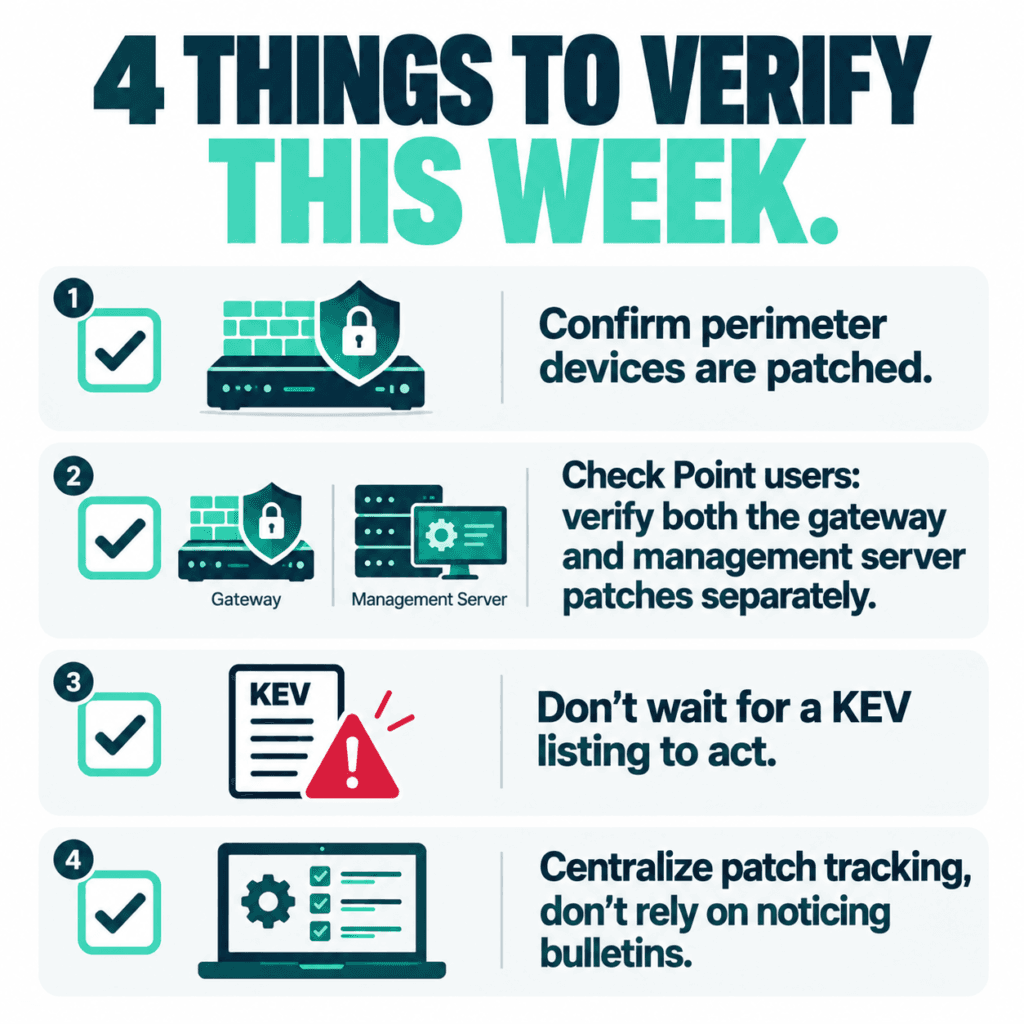
Confirm perimeter devices, firewalls, VPN gateways, remote access appliances, and their management consoles, are on the vendor’s current patched build, not just “up to date” by whatever definition IT last used.
If you run Check Point, verify both patches separately. The gateway fix and the management server fix are not the same update.
Don’t wait for a CISA KEV listing to treat a critical severity rating as urgent. By the time it’s confirmed exploited, the window has already closed for some businesses.
Check whether patch management is actually tracked somewhere, or whether it depends on someone noticing a vendor bulletin. If it’s the second one, that’s the actual finding from this week, not the CVE number.
If patching your perimeter isn’t something you can say with confidence is centrally tracked and verified across every device and every console, that’s worth a conversation before the next firewall vulnerability lands. Managed IT services that includes patch management as a standing part of the job closes exactly this kind of gap. It’s the same problem covered in what to ask your MSP about their own security, just from the vendor side this time.
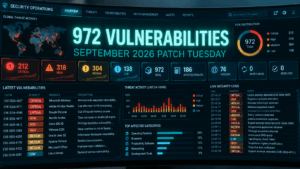
Microsoft’s September 2026 Patch Tuesday just set a record. CrowdStrike’s analysis of the release counted 972 patched vulnerabilities, more than double August’s count, and 113 of them rated Critical. Two are already being used in real attacks. If your business runs Windows anywhere, on a server, a laptop, or through a VPN, this month’s update deserves more attention than the usual “we’ll get to it”. Inside the September 2026 Patch Tuesday Release This September 2026 Patch Tuesday release patched 972 vulnerabilities in a single cycle, more than double the roughly 415 CVEs Microsoft fixed the month before, the largest release Microsoft has shipped to date. Of those, 113 carry a Critical severity rating, and two are already confirmed to be actively exploited before most businesses had a chance to patch. The volume matters less than the mix: real client-side risk in Office and Outlook, server-side risk in DNS, DHCP, and Netlogon, and infrastructure risk in Hyper-V and VPN services, all landing in the same release window. Two Vulnerabilities Are Already Being Exploited Microsoft confirmed active exploitation of two flaws before most businesses had even applied the patch. CVE-2026-81963 sits in the Windows Update Stack. CVE-2026-85880 sits in a core Windows communication component called ALPC. Both let an attacker who already has a foothold on a device, through a phishing email, a compromised browser, or stolen credentials, jump straight to full SYSTEM control. No extra clicks, no extra warnings. This is the step that turns “someone opened the wrong email” into “the attacker owns the machine.” A Dozen Office Vulnerabilities Need No Click at All Twelve of this month’s Critical fixes affect Outlook, Word, Excel, and PowerPoint, and they share a dangerous trait. Exploitation happens the moment a file is previewed, not opened. If Outlook’s Reading Pane or Windows’ Preview Pane is switched on, which it is by default on most machines, simply receiving a malicious email or having a crafted file land in a shared folder can be enough to run code on the device. CVE-2026-78509 (Outlook) and CVE-2026-78510 (Word) both score a full 9.8 out of 10 and fall into this category. No attachment to open. No macro to approve. No click required. Core Business Infrastructure Was Also Exposed This wasn’t only a desktop software patch cycle. Critical, unauthenticated remote code execution flaws landed in DNS Server, DHCP Server, Netlogon, and Kerberos, the services that handle domain logins, network addressing, and authentication for any business running Windows Server and Active Directory. Hyper-V and the built in SSTP VPN service were also patched for flaws that let an attacker escape a virtual machine or breach an internet facing VPN gateway directly. Left unpatched on exposed infrastructure, any one of these is a realistic path to a full network compromise, not just a single device. The Patching Doesn’t Stop at Microsoft’s Fix Roughly two hours after this month’s patches went out, a security researcher published a new proof of concept targeting Microsoft Defender itself, claiming an earlier fix was incomplete. There is no patch available for it yet. It’s a reminder that a Patch Tuesday release isn’t the finish line for a given month’s risk. It’s the starting point for what still needs watching. What This Means Without a Dedicated IT Team? A record setting patch release is exactly the kind of month where “we’ll update everything next time we’re in the office” gets expensive. Two of these flaws are already being exploited, and a handful more are one proof of concept away from the same fate. This is the gap that managed IT and cybersecurity support exists to close, especially in a month like this September 2026 Patch Tuesday release. Patches get assessed, prioritized by real risk instead of by however Windows Update happens to sort them, and applied on a schedule that doesn’t depend on someone remembering to click Update between meetings. Table of Content 1 Inside the September 2026 Patch Tuesday Release 2 Two Vulnerabilities Are Already Being Exploited 3 A Dozen Office Vulnerabilities Need No Click at All 4 Core Business Infrastructure Was Also Exposed 5 The Patching Doesn’t Stop at Microsoft’s Fix 6 What This Means Without a Dedicated IT Team?
The most useful questions to ask your MSP right now have nothing to do with your own network. They are about the tools your provider uses to reach into it. On September 11, 2026, the U.S. Cybersecurity and Infrastructure Security Agency added a critical ConnectWise ScreenConnect vulnerability to its Known Exploited Vulnerabilities catalog after confirming that attackers were already using it in real attacks. ScreenConnect is one of the most widely used remote support platforms in the managed services industry, which means the story is not really about one product. It is about a category of tools that sit at the center of how nearly every managed IT provider reaches into a client’s network. For a small or mid-sized business, the useful takeaway is not which specific vulnerability appeared this week. It is a short set of questions to ask your MSP so you understand how they secure the tools they use to reach you. What Actually Happened With ScreenConnect? The flaw, tracked as CVE-2026-84869, is an improper privilege management and missing authorization issue. In practical terms, it could allow an attacker to transfer files to a device and execute them during an active remote support session without the host user ever approving the action. CISA set a remediation deadline of September 14, 2026, for federal agencies covered by Binding Operational Directive 26-04, and the same urgency applies to any organization running the affected version. The specific patch was straightforward for providers who noticed. The harder question sits one level up: how confident is your provider in their ability to spot, patch, and respond to something like this on their own infrastructure, not just on yours? Why This Matters for Small Businesses? Managed service providers are built on trust and access. A single provider often holds administrative reach into dozens or hundreds of client environments using remote support tools, remote monitoring platforms, and centralized password vaults. That concentration of access is efficient for delivery, and it is also exactly why attackers have been aiming at the provider layer rather than at each client individually. According to the Huntress 2026 Cyber Threat Report, abuse of remote monitoring and management tools now accounts for 24% of all observed incidents, up from 7% the year before. Huntress’s own analysis flagged ScreenConnect specifically, including one case where a rogue install sat quietly for five months before an attacker used it as an entry point. The ScreenConnect entry in the KEV catalog is not an isolated event. It is the latest example of a documented, ongoing trend, and it is why the cybersecurity posture of your provider now matters as much as your own, which is exactly why the questions to ask your MSP have shifted this year. 5 Questions to Ask Your MSP If you already have a managed IT provider, or you are evaluating one, these are the questions to ask your MSP directly. Good providers will have clear, unrehearsed answers. 1. How quickly do you patch the tools you use to reach my network? Ask about their patch cadence for their own infrastructure, not just yours. A provider running weekly patch cycles internally is in a very different position than one that treats their tools as “set and forget.” Our September Patch Tuesday breakdown shows how quickly critical fixes can pile up in a single month. 2. What monitoring do you have on your own remote sessions? Session logging, anomaly detection, and alerting on unusual remote access patterns should all exist on the provider side. If they cannot describe what triggers an alert on their own systems, that is a signal worth paying attention to. 3. Do you enforce multi-factor authentication on every tool that reaches my environment? Every account, every technician, every tool. Not “we use MFA on email.” MFA on the remote support platform, on the RMM console, on the password vault, and on any cloud dashboard that touches client data. Enterprise-grade password managers make this practical to enforce at scale. 4. What is your response plan if one of your own accounts is compromised? The right answer is not “that would not happen.” The right answer is a specific set of steps: session revocation, credential rotation, client notification timelines, and a documented containment playbook. This should also connect back to whatever cybersecurity insurance obligations exist on either side. 5. Are you aligned to a recognized security framework internally, not just for compliance reporting? Frameworks like the NIST Cybersecurity Framework 2.0 and the CIS Controls exist for exactly this reason. A provider who applies these internally, not only when a client asks about compliance, is thinking about their own posture the same way they think about yours. What to Do Next? If you already have a managed IT provider, send these five questions in a short message and see how they respond. The quality of the answer matters as much as the content: unrehearsed and specific beats polished and vague every time. If you are weighing options, bring these questions to ask your MSP into the conversation before you sign anything. A provider who treats these questions as reasonable and expected is showing you how they operate. One who deflects is also telling you something. At Pexo, security posture starts with the tools we use before it reaches the networks we protect. If you are evaluating your options, our managed IT services team is happy to walk you through exactly how we answer each of these questions for our own environment. Table of Content 1 What Actually Happened With ScreenConnect? 2 Why This Matters for Small Businesses? 3 5 Questions to Ask Your MSP 3.1 1. How quickly do you patch the tools you use to reach my network? 3.2 2. What monitoring do you have on your own remote sessions? 3.3 3. Do you enforce multi-factor authentication on every tool that reaches my environment? 3.4 4. What is your response plan if one of your own accounts is compromised? 3.5 5. Are you aligned to a recognized security
Cybersecurity has a wide scope and ultimately refers to numerous types of security targeting different problems. However, at the same time, the dependency of the world on technology is exposing us to many risks. Cyber threats (ransomware, phishing, breaches, etc.) remain some of the biggest sources of business risks. To be safe, one of the things a business has to do is to be aware of the ways of protecting different areas of security, making them strong and safe. 7 Types of Cyber Security 1. Network Security Network security primarily involves securing the communication channels and the computer networks of an enterprise. It aims to prevent unauthorized access, misuse, malfunction, modification, destruction, or improper disclosure of the networks. Many businesses use the internet to communicate and operate their systems and software. This is why it is so important to have adequate network security in place; otherwise, any hacker could gain access to the business and their confidential information or cause a disruption in their operations. 2. Application Security Application security covers, in particular, the software, applications, and web apps side of the business. It reaches the different points, such as lines of code, servers, and platforms, where cyber threats and vulnerabilities can get through. The primary focus here is on preventing data or code within the app from being stolen or hijacked. Aside from physical checks, it can be done by applying some security patches or encryption. 3. Cloud Security With more and more companies putting data and operations on the cloud, cloud security has become more crucial than ever before. It is concerned with protecting data, applications, and storage services hosted in a cloud. If cloud security is not implemented, organizations could experience data security, compliance, and cash losses. 4. Endpoint security It ensures protection for devices like laptops, mobiles, tablets, and servers that are connected to a network system. Given the widespread adoption of remote and hybrid work, many endpoints are increasingly being seen as a prime target by cyber criminals, by way of malware, ransomware, and phishing. 5. Information security It refers to protecting critical information (whether in storage or in transition) from many threats to ensure the availability, integrity, and confidentiality of the information. It maintains the privacy, integrity, and availability of business information. This covers protecting the customer records, financial data, contracts, and business documents through encryption, access controls, and backup systems. 6. Operational Security Maintaining operational security means developing the policies and procedures for managing and safeguarding sensitive business information. Cybersecurity of this nature restricts who may store, use, or disclose the data of a company. Companies that carry out solid operational security measures are less prone to facing insider risks or accidentally exposing data. 7. Disaster Recovery and Business Continuity Besides causing damage to a company’s reputation, cyberterrorism may also lead to a complete malfunction of the business. Disaster recovery, plus business continuity measures, enables companies to bounce back swiftly in case of a breach of security. Why Do Businesses Need Cyber Security? Protection Against Data Breaches Growing clients’ and firms’ data repository is the first step toward becoming a potential hacker’s target. Cybersecurity measures provide a barrier against the theft of, /misuse of, and access to sensitive information by users without proper authorization. Financial Loss Prevention A cyberattack can cause huge financial losses through downtime of the system, fines from courts, cost of restoration, and loss of image. Implementing robust security measures can help a business prevent such expensive mishaps. Customer Trust and Brand Reputation Customers trust companies with their personal data and expect them to safeguard it. Even one breach can ruin the company’s reputation and cause a decline in customers’ faith. Having cyber security measures in place is a way of honoring that trust and maintaining one’s position in the market. Compliance With Regulations Disregarding compliance with data protection laws and cybersecurity regulations often means penalties, legal actions, and loss of reputation. Protection From Evolving Threats Attackers are always finding new ways to exploit vulnerabilities, leveraging AI to conduct phishing, ransomware, and identity theft among other tactics. Cybersecurity solutions need to be up-to-date to be effective against current threats. Pexo Offers Cyber Security Services That Provide Smart and Reliable Cyber Defense Pexo Cyber Security Services provides advanced cybersecurity solutions that not only protect a business from cyber threats of the 21st century but also help the enterprise to comply with the regulations and secure its operations. Conclusion Cybersecurity cannot be limited to a single aspect. For example, network security, cloud security, or disaster recovery are lockdown measures in different dimensions of the organization. Securing operations vulnerable to intrusions, safeguarding the company’s sensitive information, and reassuring customers are three very important aspects of cybersecurity. Table of Content 1 7 Types of Cyber Security 1.1 1. Network Security 1.2 2. Application Security 1.3 3. Cloud Security 1.4 4. Endpoint security 1.5 5. Information security 1.6 6. Operational Security 1.7 7. Disaster Recovery and Business Continuity 2 Why Do Businesses Need Cyber Security? 3 Conclusion
Monil Saheba, Pexo's CEO, shapes business resilience through technology. He leads teams redefining IT with strategic support and cybersecurity, empowering organizations to harness technology for innovation and success.