Cyber Security Awareness Month: 4 Smart Habits for Teams
Cyber Security Awareness Month: 4 Smart Habits for Teams
Every October, Canada marks Cyber Security Awareness Month, and the 2026 theme from the Government of Canada’s Get Cyber Safe campaign is “Your best defense is you.” For a business owner, that line describes how most attacks actually succeed. Firewalls, backups and updates all matter, but a single employee deciding whether to click, reply or share is often the last line of defense.
This year’s campaign adds a new twist. Artificial intelligence is making scams look more real, so phishing emails and fake messages are harder to spot than the old ones full of spelling mistakes. That is why Cyber Security Awareness Month 2026 puts habits ahead of checklists. A team that pauses by default is harder to fool than a team trying to remember a list of warning signs.
What Cyber Security Awareness Month 2026 Asks of Your Team
Get Cyber Safe splits October into four weekly themes: recognize cyber threats, strengthen your defences, protect your information and build your cyber security community. Cyber Security Awareness Month speaks to everyone, but each of its themes maps neatly onto something a small business can do with its own staff.
The numbers behind it explain the urgency. In the campaign’s 2026 tracking survey of Canadians, 59% reported at least one cyber incident in the past year, 73% said they are concerned about cybercrime involving AI, and only 42% felt confident they could recognize AI generated content. Those are figures for the general public, not for businesses, but your employees are part of that public.
Here are four habits to build with your team this month, one for each weekly theme. None of them requires new software.
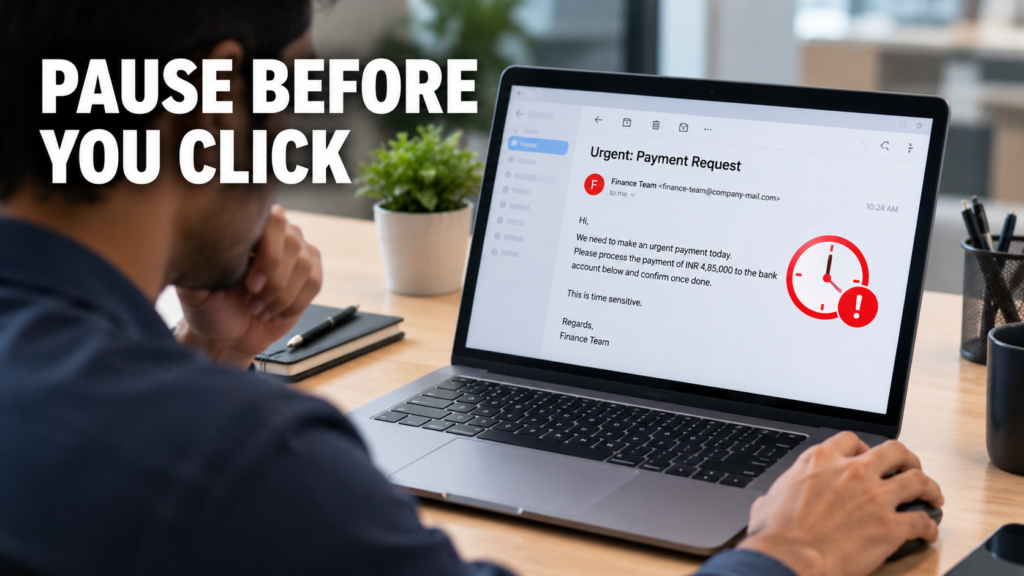
Habit 1: Pause Before You Click, Reply or Share
Convincing scams lean on urgency: an invoice that must be paid today, an executive asking for gift cards, a shared document that needs a login. Agree on one rule for the whole team. If a message asks for money, passwords or sensitive files, confirm it through a second channel, such as phoning the sender on a number you already have, not one printed in the message.
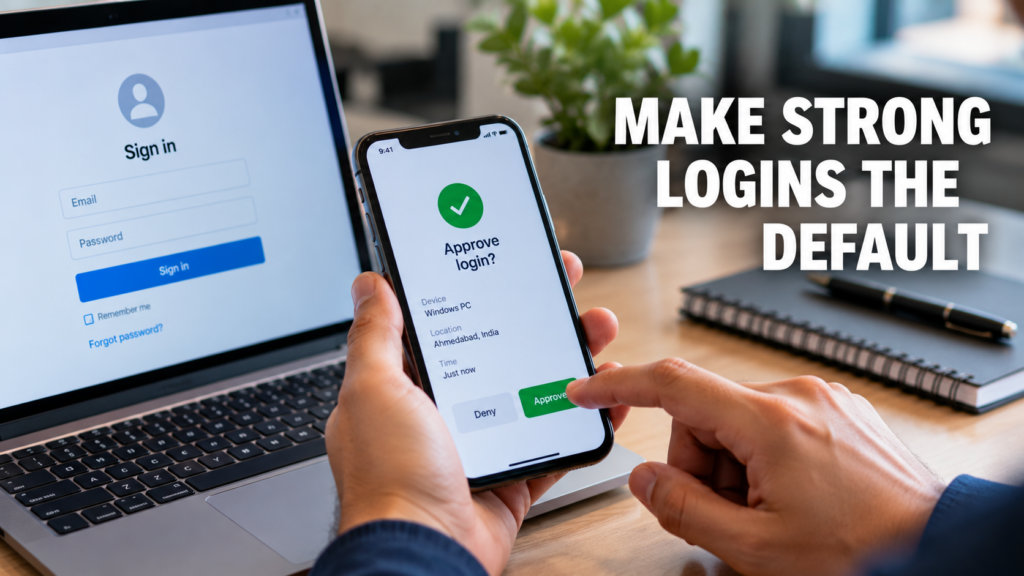
Week two of Cyber Security Awareness Month covers strong passwords, password managers and multi-factor authentication (MFA). For a business, the important word is default. In a 2026 survey of 1,000 US small and mid-sized business leaders by the National Cybersecurity Alliance and CISA, 86.8% had implemented MFA, but only 51.1% required it on all key business accounts. The accounts that get skipped are often the ones attackers want most, such as email, accounting software and remote access.
List your key accounts this week, turn MFA on for every one, and give staff a password manager so that using a unique password is easier than reusing one. If you are weighing options, our guide to what makes a password manager enterprise-grade explains what to look for.
Habit 3: Keep Business Information Where It Belongs
Week three of Cyber Security Awareness Month is about protecting information, and in Canada it also falls on Small Business Week. Get Cyber Safe has a quick guide to cyber security for small business worth sharing with your team. For a business, protecting information comes down to three questions: who can see it, where does it go, and can we get it back?
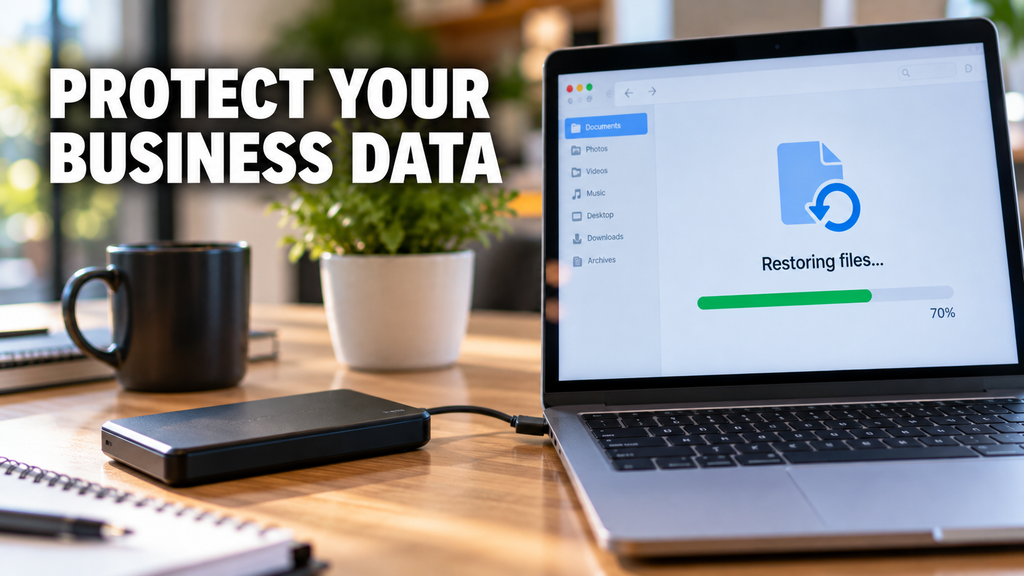
Two gaps stand out in the same US survey. AI use among small businesses reached 87.3%, but only 45.6% had formal guidelines for it. A one page rule is enough to start: no customer data, financial records or contracts go into free public AI tools. And while 88.4% of businesses had backups, only 61.4% had tested them. Schedule a test restore this month, so you learn whether your backup works before you need it.
Habit 4: Make Reporting Normal
The final theme is about building a community and reporting scams and fraud. Inside a business, that means the most valuable thing an employee can do with a suspicious message is tell someone quickly, without fear of blame. Pick one place for reports, such as a shared mailbox or a chat channel, and make sure everyone knows it.
Pair that with a one page incident plan: who gets called first, which devices get disconnected, and who speaks to clients. The same survey found that organizations that had been breached were far more likely to have a documented response plan than those that had not (74.9% against 51.5%), which suggests many businesses write theirs only after something goes wrong. Short, regular training helps too, and 42.4% of those leaders named short employee training as a priority.
Turning One Month Into a Habit
You do not need to do everything at once. Take one habit a week, start each with a short conversation, and put a reminder in the calendar so the habit outlasts Cyber Security Awareness Month. These habits also cover many of the basics that cyber insurance applications tend to ask about, so they are worth writing down. Our cybersecurity insurance questionnaire is a quick way to see where you stand.
If you would like help putting any of this in place, we support small businesses across Markham and the GTA with cyber security and managed IT services. Get in touch and we will walk you through where to start.
With businesses increasing digital, cybersecurity is no longer a mere IT issue; it is a key business priority. The year is 2026, and the world of cybersecurity has undergone significant transformation. Security teams must remain vigilantly initiative-taking to protect their organizations from data breaches, and all types of organizations are target for attack. The following are the six key cybersecurity trends shaping 2026 that will help your business know what risks to prepare for and how best to approach them with resilient security strategies. The Disturbance – The Concept of AI-driven Cyber Threats AI is revolutionizing both ends of cybersecurity. It facilitates the speedy detection of threats but also arms cybercriminals to conduct sophisticated strikes. Attackers are increasingly using AI in 2026 too: • Backdoor phishing campaigns with highly tailored messages• More quickly discover weaknesses in systems• Evade traditional security detection tools It means businesses need AI-powered cybersecurity solutions that can recognize anomalous behavior, respond in real time, and learn constantly from new threats. Zero Trust Architecture Becomes Standard The old “trust but verify” paradigm is no longer good enough. In 2026, Zero Trust Architecture (ZTA) is now the de facto best cybersecurity practice. Zero Trust works on the zero-trust model: • Do Not Trust User or Device by Default• Continuously verify identity and access• Control access by role and need As remote tasks and cloud systems become business as usual, Zero Trust guarantees that only the right users get access to the secure data, reducing the security risks for organizations. Increased Focus on Cloud Security As cloud computing remains at the forefront of business operations, no wonder ensuring its safety will be one of the top 2026 IT security trends. Misconfigured cloud settings continue to be one of the top causes of data breaches. Businesses must focus on: • Securing cloud infrastructure and applications• Monitoring access and user activity• Encryption of sensitive cloud-based data In a world where more organizations are shifting to multi-cloud and hybrid, being able to get visibility and control across the platforms gains importance. Growing Threat of Ransomware Attacks Ransomware is still, at this stage of the game, one of the most harmful cyber threats. By 2026, these attacks will grow sophisticated and targeted. Cybercriminals are now: • Attacking essential sectors like health care, finance, and logistics• Employing double extortion (stealing data prior to encryption)• Demanding higher ransom payments It is all too easy for a business to think they cannot at least afford these, when instead they need to be investing in strong backup systems, endpoint protection, and incident response plans to minimize the impact of such attacks. The Importance of Cybersecurity Awareness Human error remains a significant risk. Even the best systems can fail if employees are not trained to identify threats. In 2026, organizations are prioritizing: • Regular cybersecurity training programs• Phishing simulation exercises• Strong password and authentication policies Of all the things businesses can do, building a culture of security awareness is one of the most effective measures for minimizing cyber risks. Strengthening Your Cybersecurity Strategy With cyber threats becoming increasingly sophisticated, businesses must adopt an initiative-taking and holistic approach to security. Enlisting experts has an enormous impact on discovering vulnerabilities and putting the right safeguards in place. Advanced Cybersecurity Services by Pexo for Modern Enterprises Professional Cyber Security Services offered by Pexo are essential for organizations aiming to stay proactive and strengthen their cybersecurity posture. Our diverse expertise, ranging from cybersecurity risk assessments to advanced threat monitoring solutions, ensures that you have the right cybersecurity partner to support your business in an ever-evolving threat landscape. Regulatory Compliance and Data Privacy Countries across the globe are clamping down on data protection. AQUISITION Since 2026 compliance is not optional, it is necessary. Businesses must ensure: • How to manage and store data properly• Transparent privacy policies• Regional and global regulatory compliance Non-compliance carries hefty fines and harm to brand reputation. IoT Security Risks: New Attack Surface Internet of Things (IoT) is growing fast and connects devices in various sectors. But every connected device provides a potential gateway for cyberattacks. In 2026, businesses must: • Secure all connected devices• Regularly update firmware and software• Look for anomalies in network activity Now IoT security is crucial in the overall CIS strategy. Conclusion Cyber Security in 2026: The Future of Cybersecurity in Vision for 2026 As business moves away from reaction to initiative-taking intelligent security. With the help of AI-powered tools, incorporating Zero Trust models into their security strategy, making sure that their cloud environments are safe and taking an initiative-taking approach to raising employee awareness – organizations can remain one step ahead of cyber risks. Cybersecurity is beyond protection, it is about trust, continuity, and sustainable growth in a digital era. Frequently Asked Questions (FAQs) Table of Content 1 The Disturbance – The Concept of AI-driven Cyber Threats 2 Zero Trust Architecture Becomes Standard 3 Increased Focus on Cloud Security 4 Growing Threat of Ransomware Attacks 5 The Importance of Cybersecurity Awareness 6 Strengthening Your Cybersecurity Strategy 7 Advanced Cybersecurity Services by Pexo for Modern Enterprises 8 Regulatory Compliance and Data Privacy 9 IoT Security Risks: New Attack Surface 10 Conclusion 11 Frequently Asked Questions (FAQs)
In a world where everything is so connected, right from banking and shopping to business operations – cybersecurity is no more optional. Every login, click and transfer of data has potential risk. Cybercriminals are consistently looking for susceptibilities, and this is the reason understanding the various kinds of cybersecurity is required for businesses and individuals in same manner. Cybersecurity is not a single software or tool. It is a layered approach that shields networks, applications, data and systems from all kinds of unauthorized attacks, damages and access. Kinds Of Cybersecurity And Examples Let’s know about five major kinds of cybersecurity, along with some examples to know how they function in real life. 1. Network security Network security focuses mainly on protection of computer network from unauthorized access of users, cyberattacks and data breaches. As maximum digital communication occurs over networks, this is one of the most important layers of cybersecurity. Critical elements: Examples: Think of a company that installs a firewall for monitoring incoming and outgoing traffic. In case a hacker attempts for accessing the system, the firewall blocks the request and prohibits unauthorized entry. Importance: In absence of a strong network security, it becomes easy for attackers to infiltrate systems, steal sensitive data and cause disruptions in operations. 2. Application Security Application security includes protection of software and applications from threats at the time of development and post development. Since apps often manage sensitive data, they are common targets for cyberattacks. Important elements: Example: An online shopping application make use of safe login methods and regular updates are done for fixing bugs. This prohibits hackers from exploiting weaknesses for accessing consumer data. Importance Even a minor vulnerability in any application can result in huge data breaches or compromise of system. 3. Information security Information security focuses mainly on protection of data from corruption, theft or any unauthorized access. It make sure that all sensitive data stays confidential and accessible only for authorized users. Important elements: Example: A healthcare center encrypting records of patients so that only certified doctors and staff can get access to them, making sure there is compliance and privacy. Importance: One of the most valuable assets today is data. Losing it can result in loss of finances, damage to reputation and legal outcomes. 4. Cloud security As businesses are moving more and more to cloud platforms, importance of cloud security is also increasing. It focuses on protection of data, applications and services that are hosted in cloud environments. Important elements: Example: A company storing files on the cloud allows multi-factor authentication. Even when somebody gets the password, they can’t get access to the account without extra verification. Importance: Cloud platforms store big volumes of sensitive data, which makes them strong targets for cybercriminals. 5. Endpoint security Endpoint security shields devices like laptops, desktops and smartphones that connects to a network. With remote work becoming more and more common, keep these devices safe is important. Important elements: Example: An employee laptop is well-equipped with antivirus software that finds and eliminates malicious files before they cause any harm to the system or spreads to the network. Importance: Each connected device is a potential entry point for attackers. Weak endpoints can cause compromise of the whole system. Importance Of Multi-Layered Approach No single kind of cybersecurity can offer full protection. Cyber threats are consistently evolving and attackers often cause exploitation of various vulnerabilities at a single time. This is the reason, all five kinds can create a strong defense system. Like for instance, even when you have a safe network, a weak application or any unprotected device can cause exposure of your data. A multi-layered approach make sure that when one layer fails, other continue to give protection to your system. Keep Your Cybersecurity Strong With Expert Support Protecting your business from cyber threats needs more than any basic tools. It needs a planned and proactive approach. If you are searching for a dependable and latest protection, professional cybersecurity services can bring in all difference. The Solutions offered by Pexo it consluting assists businesses in recognizing vulnerabilities, execute strong safety measures and stay ahead of evolving threats. Right from risk assessment to real time tracking, investment in expert cybersecurity support make sure your data, systems and reputation stays safe. Conclusion Cybersecurity is a necessity in present day digital landscape. The five important kinds- network security, application security, information security, endpoint security and cloud security- each play a vital role in protection of your digital atmosphere. Understanding those categories assists in building a strong defense against cyber threats. Whether you are an individual user or you are running a business, staying well-informed and proactive is one of the best way for staying safe. Table of Content 1 Kinds Of Cybersecurity And Examples 1.1 1. Network security 1.2 2. Application Security 1.3 3. Information security 1.4 4. Cloud security 1.5 5. Endpoint security 2 Importance Of Multi-Layered Approach 3 Keep Your Cybersecurity Strong With Expert Support 4 Conclusion
In today’s digital world, technology is integral to our everyday lives. People use it for banking, communication, shopping, the Storage of Critical Data, etc. These technologies, though, can be a source of vulnerability and opportunity for the cybercriminal. Cyber attacks are a growing threat to medium, small, and large businesses across every sector. What is a Cyber Attack? A cyber attack is an intentional act of hackers or cybercriminals used to gain access to a computer system, network, or information system without the permission of the owner. Cyber-attacks attempt to steal information, damage, or even shut down a computer system. Cyber attacks take many forms that entail the following: How Does a Cyber Attack Happen? If you know the way in which the attacks are made, it will provide a good opportunity for the organizations to enhance their habitudes so that they can be as secure as possible and minimalizing the risks to be caught up in the cyber attacks. Phishing Emails Phishing is still one of the main ways in which criminals fool people. Cybercriminals will send very deceptive emails that are faked to look like those from well-known companies or from people you might trust. Weak Passwords Using the same weak password over and over again makes it easier for hackers to gain access to your accounts. Cybercriminals can guess passwords using automated tools and will then try to get access to your system or application without your permission. Malware and Ransomware Malware refers to any kind of malicious software that is designed to cause harm to a computer or to steal data. Ransomware is a form of malware whereby files or systems are locked until a ransom is paid. In most cases, a user is duped into downloading malware or is sent a suspicious attachment. Software Vulnerabilities Cyber attackers are known to exploit security loopholes in old software or operating systems. If an organization fails to apply security patches or install updated versions of their software, then it is as if to invite the hackers who are capable of using these vulnerabilities to break into their networks without authorization. Unsafe Public Wi-Fi You should not even consider using an unsecured public Wi-Fi as it is extremely easy for a cybercriminal to attack you. Their actions may even consist of observing your Internet traffic and, at the same time, stealing your passwords, bank account information, or other types of sensitive data that you may be sending while you are still on an unprotected connection. How to Avoid a Cyber Attack? Be sure to create a strong password Make your passwords longer and more complicated by combining letters, numbers, and different symbols. Avoid using the same password for different accounts. Also, use multi-factor authentication whenever it is available. Keep Software Updated You should upgrade your computer’s operating system as well as your apps and anti-virus program quite often. This way, vulnerabilities will not only be patched, but also the level of protection will be raised to counter new threats. Train Employees Human error accounts for a significant portion of cyberattacks. Companies need to offer training to their staff members on how to spot phishing emails, handle suspicious messages, and perform online activities safely to lessen the vulnerability to such attacks. Install Reliable Security Software Antivirus software, firewalls, and endpoint security solutions form the first line of defense by detecting and preventing the running of malicious code that the attackers use to harm your computers. Backup Important Data By backing up data, businesses, are able to survive the aftermath of a ransomware attack or any incident of data loss. They must keep the backup copies in safe locations and carry out their verification regularly and thoroughly. Avoid Suspicious Links and Attachments Generally, interacting with strange links, downloading files from untrusted sources, or even opening suspicious mail attachments should be completely avoided by users. One of the security habits is to always check the sender’s credibility before replying to emails. Nowadays, companies are exposed to numerous cyber threats that call for sophisticated protection measures together with regular surveillance. Pexo offers extensive cybersecurity services to help enterprises recognize threats, prevent attacks, and protect sensitive information. Conclusion To sum up, hacking is a very serious issue in the tech world that not only harms individuals but businesses too. Knowing what hacking is, in case it is perpetrated, and effective ways to stop it are among the factors that can greatly minimize one’s exposure to data theft and monetary fraud. Table of Content 1 What is a Cyber Attack? 2 How Does a Cyber Attack Happen? 3 How to Avoid a Cyber Attack? 4 Conclusion
Monil Saheba, Pexo's CEO, shapes business resilience through technology. He leads teams redefining IT with strategic support and cybersecurity, empowering organizations to harness technology for innovation and success.